
How to start a payment processing business in 2026
May 13, 2026
TL;DR:
- Owning your payment processing infrastructure offers retailers a competitive edge by controlling costs and ensuring seamless checkouts.
- Successful implementation requires careful selection of a business model, compliance with standards, and robust merchant support processes.
Owning your payment processing infrastructure gives retailers and eCommerce operators a real competitive edge, from controlling transaction costs to delivering a seamless checkout experience across every sales channel. But the path from idea to operational processor is demanding. It requires choosing the right business model, meeting strict compliance standards, building or integrating reliable technology, and setting up airtight merchant support. This guide walks you through each essential step, so you can move forward with clarity and avoid the costly mistakes that derail most first-time entrants.
Table of Contents
- Understand payment processing business models
- Prepare your operational and compliance framework
- Build or integrate your payment technology
- Establish onboarding, risk management, and support processes
- The realities most guides skip: Lessons from the front lines
- Ready to launch your payment processing solution?
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Choose the right model | ISO, PayFac, or ISV models have different operational and compliance demands. |
| Secure sponsors and compliance | You’ll need acquirer sponsors, proper registrations, and must manage PCI DSS and legal requirements. |
| Prioritize technology integration | Building or connecting to leading APIs and POS systems expands your business reach. |
| Emphasize risk and merchant support | Effective onboarding, anti-fraud, and support processes are crucial for reputation and security. |
| Plan for real-world complexity | Success depends on nailing vendor contracts, ongoing education, and adapting compliance, not just technology choices. |
Understand payment processing business models
Before you write a single line of code or sign a contract, you need to decide which business model fits your goals. There are three primary paths: the ISO model, the PayFac model, and the ISV model. Each one carries a different level of risk, operational complexity, and revenue potential, and your choice will shape everything that follows.
ISO (Independent Sales Organization): An ISO acts as a reseller of payment processing services. You sign a sponsorship agreement with an acquiring bank, then sell processing capabilities to merchants under that relationship. The acquiring bank handles most of the compliance heavy lifting, and your role is primarily sales and account management. ISOs typically earn residuals on transaction volume. To start a payment processing business, you must choose a payments model and secure the sponsor or acquiring relationship required for that model, whether that’s an ISO with an acquirer sponsor or a PayFac registration via a sponsor.
PayFac (Payment Facilitator): A PayFac onboards sub-merchants under its own master merchant account. You take on more liability and underwriting responsibility, but you also gain much greater control over the merchant experience, pricing, and data. PayFac registration is more involved, often requiring money-transmitter licensing and PCI DSS compliance. The revenue ceiling is higher, but so is the operational burden.
ISV (Integrated Software Vendor): An ISV embeds payment processing directly into a software product, such as a point-of-sale (POS) system or an eCommerce platform. This model suits companies that already have a software product and want to monetize payments as part of their offering. ISVs often partner with a PayFac or ISO rather than going fully independent.
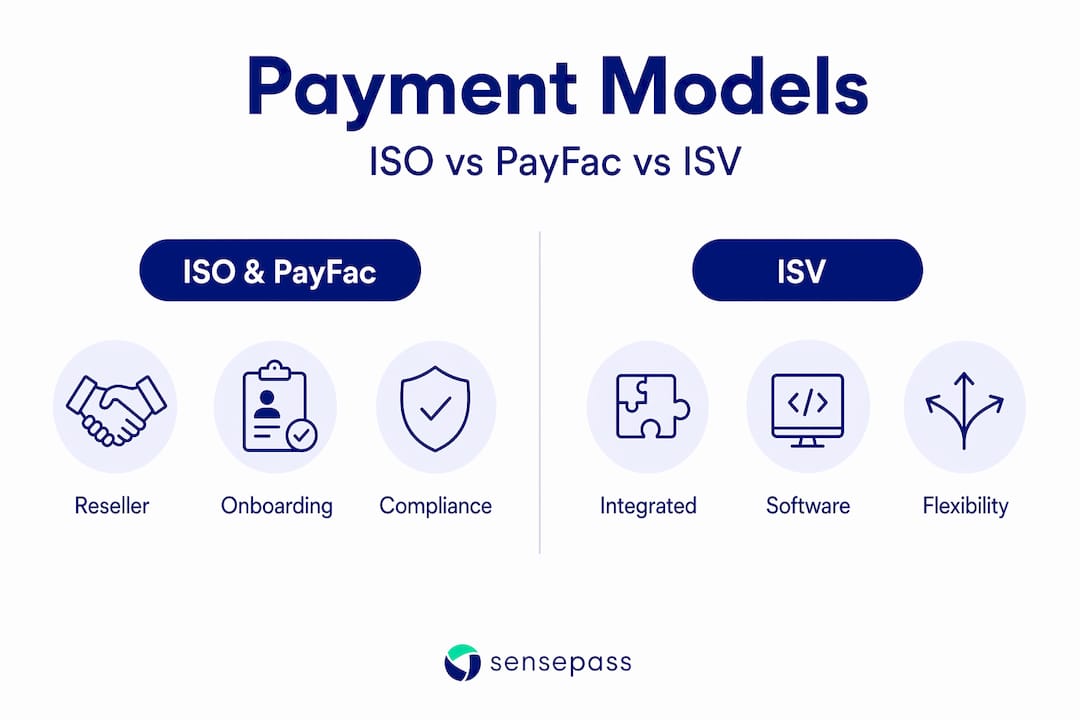
Here is a quick side-by-side comparison:
| Model | Compliance burden | Revenue control | Setup complexity | Best fit |
|---|---|---|---|---|
| ISO | Low to medium | Medium | Low | Resellers, agents |
| PayFac | High | High | High | Platforms, SaaS |
| ISV | Medium | Medium | Medium | Software vendors |
Understanding retail payment models before making a commitment saves significant time and money. The processor integration differences between these models also affect what your merchants can do at the register and online, so choose based on your long-term roadmap, not just what is easiest to launch.
Key considerations for POS and eCommerce operators:
- If you are building a platform that serves brick-and-mortar retailers alongside an online store, the PayFac or ISV model typically offers the most integration flexibility.
- ISO works best when you want to launch fast with lower overhead and are comfortable relying on your sponsor bank’s infrastructure.
- ISV is ideal if you already have POS software and want to add native payment functionality rather than redirecting users to a third-party checkout.
Pro Tip: Talk to at least two or three acquiring banks before committing. Each sponsor bank has different appetite for certain merchant categories, and their terms will directly affect your margins and what merchant types you can serve.
Prepare your operational and compliance framework
Once you choose your business model, set up your operations and tick off compliance requirements before building or buying tech. This stage is where many new entrants lose momentum, not because the tasks are impossible, but because they underestimate the volume of documentation, legal review, and vendor coordination involved.
Sponsor and acquirer requirements:
- Identify an acquiring bank willing to sponsor your model. This relationship is the foundation of your payment processing capability.
- Submit a business plan, financial statements, and a risk management overview to the acquiring bank.
- For ISO registration, complete the card network registration process with Visa, Mastercard, or both.
- For PayFac registration, expect a deeper review process covering underwriting policies, fraud controls, and reserve fund commitments.
- Document your sub-merchant onboarding process, including Know Your Customer (KYC) and anti-money laundering (AML) procedures.
PCI DSS and shared responsibility:
PCI DSS (Payment Card Industry Data Security Standard) is not optional. Depending on your model and how you handle cardholder data, you may fall into SAQ (Self-Assessment Questionnaire) categories or require a full QSA (Qualified Security Assessor) audit. PCI compliance in 2026 increasingly requires that you plan for shared-responsibility and vendor accountability. Your compliance posture depends on the POS, gateway, and processor contracts your business signs and their individual certification readiness.
“PCI compliance is not a one-time checkbox. It is a continuous operational discipline that requires regular review of every vendor, device, and data flow in your payment stack.”
Core compliance documents you need:
- Merchant services agreement (MSA)
- Data processing agreement (DPA) aligned with applicable state and federal privacy laws
- Card network registration certificates
- AML and KYC policy documents
- Incident response plan for data breaches
Building acquirer relationships early also gives you access to fraud intelligence and underwriting guidance that you simply cannot replicate by reading policy documents alone. And do not overlook payment security best practices at the device level, especially for in-store POS environments where physical tampering is a real risk.
Build or integrate your payment technology
You have squared away the business structure and compliance. Now it is time to make technology choices that determine what retailers and shoppers actually experience at checkout. This is where the investment starts to feel real, and where shortcuts tend to create the most expensive long-term problems.
Build vs. integrate:
The core decision is whether you build proprietary payment software or integrate with an existing gateway or API. Most operators starting out choose integration first, then consider building proprietary components as volume and revenue justify the investment.
ISV approaches focus on integration with checkout flows in the software layer, meaning your payment feature set is largely determined by which gateway or processor API you connect to. This makes gateway and API selection one of the most consequential technology decisions you will make.
What to evaluate in a payment gateway or API:
- Supported payment methods: cards, digital wallets (Apple Pay, Google Pay, PayPal, Venmo, WeChat, Alipay, Amazon Pay), BNPL options (Klarna, Afterpay, Sezzle, ZIP, Splitit), financing (Affirm, WeGetFinancing), crypto (BitPay, Coinbase), and Pay by Bank options (Trustly, LinkMoney)
- POS system compatibility: does the API support the hardware and software your target merchants already use?
- Tokenization and encryption standards for secure card storage
- Reporting and reconciliation tools merchants can actually use day-to-day
- Developer documentation quality and sandbox environment availability
Integration checklist:
- Confirm certification status for targeted POS terminals (EMV, NFC, contactless)
- Verify card network compliance for online checkout integrations
- Test the API in a sandbox environment with real-world transaction scenarios
- Review rate limits, uptime SLAs (Service Level Agreements), and failover options
- Map out the data flow for every transaction type to identify PCI scope
A solid payment API integration strategy accounts for more than just credit cards. Modern consumers expect flexibility, and your payment stack needs to deliver it. Use gateway selection tips to narrow down options based on your target merchant verticals before committing to a vendor.
Pro Tip: Do not evaluate gateways on feature lists alone. Run a real integration test with your most complex use case, such as a split tender transaction combining a digital wallet and a gift card, before signing any contract.
Establish onboarding, risk management, and support processes
With technical integration in place, your next priority is managing how merchants join and stay protected. This operational layer is what separates a payment processing business that scales from one that constantly fights fires.
Stepwise merchant onboarding process:
- Collect business verification documents: EIN, business license, bank account information, and ownership details.
- Run KYC and AML checks on all principals with ownership above a defined threshold (typically 25%).
- Perform underwriting review based on merchant category code (MCC), estimated volume, and chargeback history.
- Provision the merchant account and configure their payment acceptance settings.
- Ship or activate hardware if applicable, and confirm terminal certification.
- Deliver onboarding documentation and set up access to the reporting portal.
Risk management and fraud oversight:
PayFac-style models typically require more operational complexity, including underwriting, compliance, ledger management, risk controls, and chargeback handling, compared to ISO or reseller models. If you are operating as a PayFac, risk management is not a department you add later. It is a core function from day one.
Key fraud and risk controls to implement:
- Real-time transaction monitoring with configurable velocity rules
- Automated chargeback alerts and dispute response workflows
- Reserve fund policies for higher-risk merchant categories
- Periodic merchant portfolio reviews to catch emerging risk patterns
- Escalation procedures for suspected fraud or compliance violations
Merchant support structure:
Your merchants will have questions, technical issues, and disputes. If your support function is not ready at launch, expect churn to climb fast. Build a tiered support model: self-service documentation for common issues, email or chat for non-urgent requests, and phone support for high-priority situations like processing outages.
Strong credit card risk controls at the processing level also reduce the volume of issues that reach your support team. When your stack is well-configured, merchants spend less time troubleshooting and more time selling.
The realities most guides skip: Lessons from the front lines
Here is what the typical how-to guide leaves out: the majority of new payment processing ventures do not fail because of bad technology. They fail because the people building them underestimated the operational surface area they were committing to.
We have seen this pattern repeatedly. A team spends six months building an elegant payment dashboard with every feature imaginable, and then discovers they have no clear process for handling a chargeback dispute or an acquirer audit. The dashboard is impressive. The business is not ready.
The uncomfortable truth is that your vendor and acquirer agreements will define the limits of your business more than your software ever will. The terms your sponsor bank sets on reserve requirements, merchant category restrictions, and processing caps are not negotiable after the fact. Read every clause before signing, and get legal counsel that specializes in payments, not general commercial contracts.
PCI and compliance oversights are the specific category of problem that can end a payment processing business entirely. Not slow it down. End it. A single data breach that traces back to an uncertified device or an undocumented data flow can result in card network fines, acquirer termination, and reputational damage that no marketing budget recovers from. Build compliance review into your quarterly calendar, not just your launch checklist.
There is also a persistent myth that merchant onboarding is a one-time cost. In reality, onboarding never ends. Merchants need re-education when regulations change, when new payment methods are added, and when their own business models evolve. The processors that retain merchants long-term are the ones that invest in ongoing communication and support, not just the initial setup experience.
Our advice: before you write a line of integration code, spend a week mapping out your merchant lifecycle from application to offboarding, and every support touchpoint in between. That exercise will reveal gaps your technology plan never would. Review key payment features not just as a capabilities list, but as a framework for understanding what your merchants will actually need from you over time.
Ready to launch your payment processing solution?
You are now equipped with the fundamentals and hard-earned advice. The next step is putting the right tools and frameworks in place to accelerate your launch.

SensePass is built for exactly this challenge. As an orchestration layer and processor-agnostic payment gateway, SensePass integrates seamlessly with major platforms including NetSuite, SuiteCommerce, Oracle Xstore, Aptos, Shopify POS, BigCommerce, Storis, NCR, and Dynamics365. It supports digital wallets like PayPal, Venmo, WeChat, Apple Pay, Google Pay, Alipay, and Amazon Pay, BNPL options including Klarna, Afterpay, Sezzle, ZIP, and Splitit, financing through Affirm and WeGetFinancing, crypto via BitPay and Coinbase, and Pay by Bank through Trustly and LinkMoney. With access to 50+ card processors, merchants get maximum flexibility without being locked into a single stack. Explore our omnichannel payments guide and review our gateway selection strategies to find the right fit for your retail or eCommerce operation.
Frequently asked questions
What licenses are needed to start a payment processing business?
Most models require an acquiring-bank sponsor relationship as the foundation. PayFac registration may require additional money-transmitter licensing and PCI DSS compliance on top of standard card network registration.
How much does it cost to launch a payment processing business?
Startup costs scale directly with your model choice. Since model choice changes both risk/control and technology build, a PayFac setup with full compliance infrastructure costs significantly more than an ISO reseller arrangement.
How do I integrate POS systems with my payment processor?
Choose either a software-first ISV approach or a gateway API integration, then confirm POS hardware compatibility and feature support. ISV approaches focus on integration at the checkout software layer, giving you the most control over the merchant experience.
What are common mistakes when starting a payment processing business?
The most frequent failures come from underestimating compliance requirements, neglecting merchant onboarding processes, and launching without a scalable support structure. Many operators also fail to negotiate acquirer agreements carefully enough before launch, leaving themselves exposed to unfavorable terms.
How do PCI requirements apply if using third-party POS or gateways?
Your overall compliance posture is directly tied to your vendors. Your PCI compliance depends on the contracts and certification status of your POS, gateway, and processor vendors, making vendor due diligence a non-negotiable step before going live.
Recommended
- Essential Payment Gateway Selection Tips for Retailers – Omnichannel payments at the Point Of Sale | Sensepass
- Master Payment Processing Best Practices for Your Business – Omnichannel payments at the Point Of Sale | Sensepass
- How to start accepting online payments for your small business – Omnichannel payments at the Point Of Sale | Sensepass
- What Is Fast Payment Processing for Retailers – Omnichannel payments at the Point Of Sale | Sensepass

 New York Office
260 Madison Ave Suite 8018 New York NY 10016

