
Payment Security Best Practices for Omnichannel Retailers
November 4, 2025
Nearly 60 percent of data breaches involve payment systems that lack proper security controls. As cashless transactions expand, businesses face new risks that threaten customer trust and financial stability. Understanding the most common vulnerabilities and proven methods for securing your payment ecosystem is crucial for protecting every transaction—whether online, in store, or through a mobile app.
Table of Contents
- Step 1: Assess Current Payment System Risks
- Step 2: Implement Multi-Layered Payment Authentication
- Step 3: Integrate Secure Payment Gateways Like SensePass
- Step 4: Configure Omnichannel Compliance And Encryption
- Step 5: Monitor Transactions And Test Security Measures
Quick Summary
| Key Point | Explanation |
|---|---|
| 1. Conduct Comprehensive Risk Assessment | Audit your payment systems to identify security risks such as inadequate encryption and weak authentication protocols. |
| 2. Implement Multi-Layered Authentication | Use diverse verification methods like biometrics and OTPs to enhance security against fraud. |
| 3. Select Robust Payment Gateways | Choose payment gateways that offer strong encryption and fraud detection to protect transactions. |
| 4. Ensure Omnichannel Compliance and Encryption | Encrypt payment data and comply with PCI DSS to safeguard sensitive customer information. |
| 5. Monitor Transactions Continuously | Employ real-time monitoring and regular testing to detect anomalies and enhance security measures. |
Step 1: Assess Current Payment System Risks
When securing your omnichannel payment infrastructure, identifying potential vulnerabilities becomes your critical first step. According to the Comptroller of the Currency, businesses must “identify, measure, monitor, and control risk” through an effective risk management system tailored to their specific operational complexity.
Start by conducting a comprehensive audit of your current payment ecosystem. Map out every touchpoint where transactions occur online, in store, via mobile app, and through call centers. Evaluate each platform for potential security gaps such as inadequate encryption, weak authentication protocols, or outdated payment processing systems. Look for risks like:
- Unsecured network connections
- Lack of multi factor authentication
- Insufficient fraud detection mechanisms
- Potential data storage vulnerabilities
- Third party payment integration security
The Federal Reserve recommends analyzing how different risk management strategies might inadvertently shift risk between systems. This means understanding that mitigating one vulnerability could potentially expose another weakness in your payment infrastructure.
With a thorough risk assessment complete, you are now prepared to develop targeted security strategies that protect both your business and your customers’ sensitive financial information.
Step 2: Implement Multi-Layered Payment Authentication
Multi-layered payment authentication represents your strongest defense against unauthorized transactions and potential fraud. According to Fast Payments, payment service providers must establish a comprehensive security program that includes multifactor authentication, fraud detection, and robust monitoring mechanisms.
Begin by implementing multiple authentication checkpoints that validate customer identity through diverse verification methods. These can include:
- Biometric verification (facial recognition or fingerprint scanning)
- Device fingerprinting
- One time password (OTP) generation
- Geolocation tracking
- Behavioral pattern analysis
As Direct Pay Net highlights, modern authentication strategies now incorporate advanced technologies like passwordless solutions and Secure Payment Confirmation (SPC). These methods not only enhance security but also improve overall user experience by creating seamless yet robust verification processes.
Remember that your authentication strategy should balance stringent security protocols with user convenience. Overly complex authentication can deter customers, while minimal checks expose your system to potential breaches. By thoughtfully layering your security measures, you create a dynamic defense mechanism that adapts to emerging threats while maintaining a smooth transaction experience.
Step 3: Integrate Secure Payment Gateways Like SensePass
Securing your payment infrastructure starts with selecting a robust payment gateway that offers comprehensive protection across all transaction channels. According to FDIC guidelines, financial institutions must establish clear responsibility for controlling risks associated with third party payment processors, which means conducting thorough due diligence before integration.
When integrating a payment gateway like SensePass: The Next-Generation Payment Gateway, focus on several key security parameters:
- Encryption standards (TLS 1.2 or higher)
- End to end transaction protection
- Comprehensive fraud detection mechanisms
- Multi regional compliance capabilities
- Seamless integration with existing systems
Decta recommends implementing multiple protective barriers including secured network channels, encrypted data entry points, and continuous monitoring of network infrastructure. This approach ensures that your payment gateway acts not just as a transaction conduit but as a proactive security sentinel protecting your business and customer financial information.
Remember that the right payment gateway transforms from a simple transaction processor to a comprehensive security ecosystem. By carefully selecting a solution that offers advanced protection features, you create a resilient payment infrastructure that adapts to evolving digital transaction landscapes.
Step 4: Configure Omnichannel Compliance and Encryption
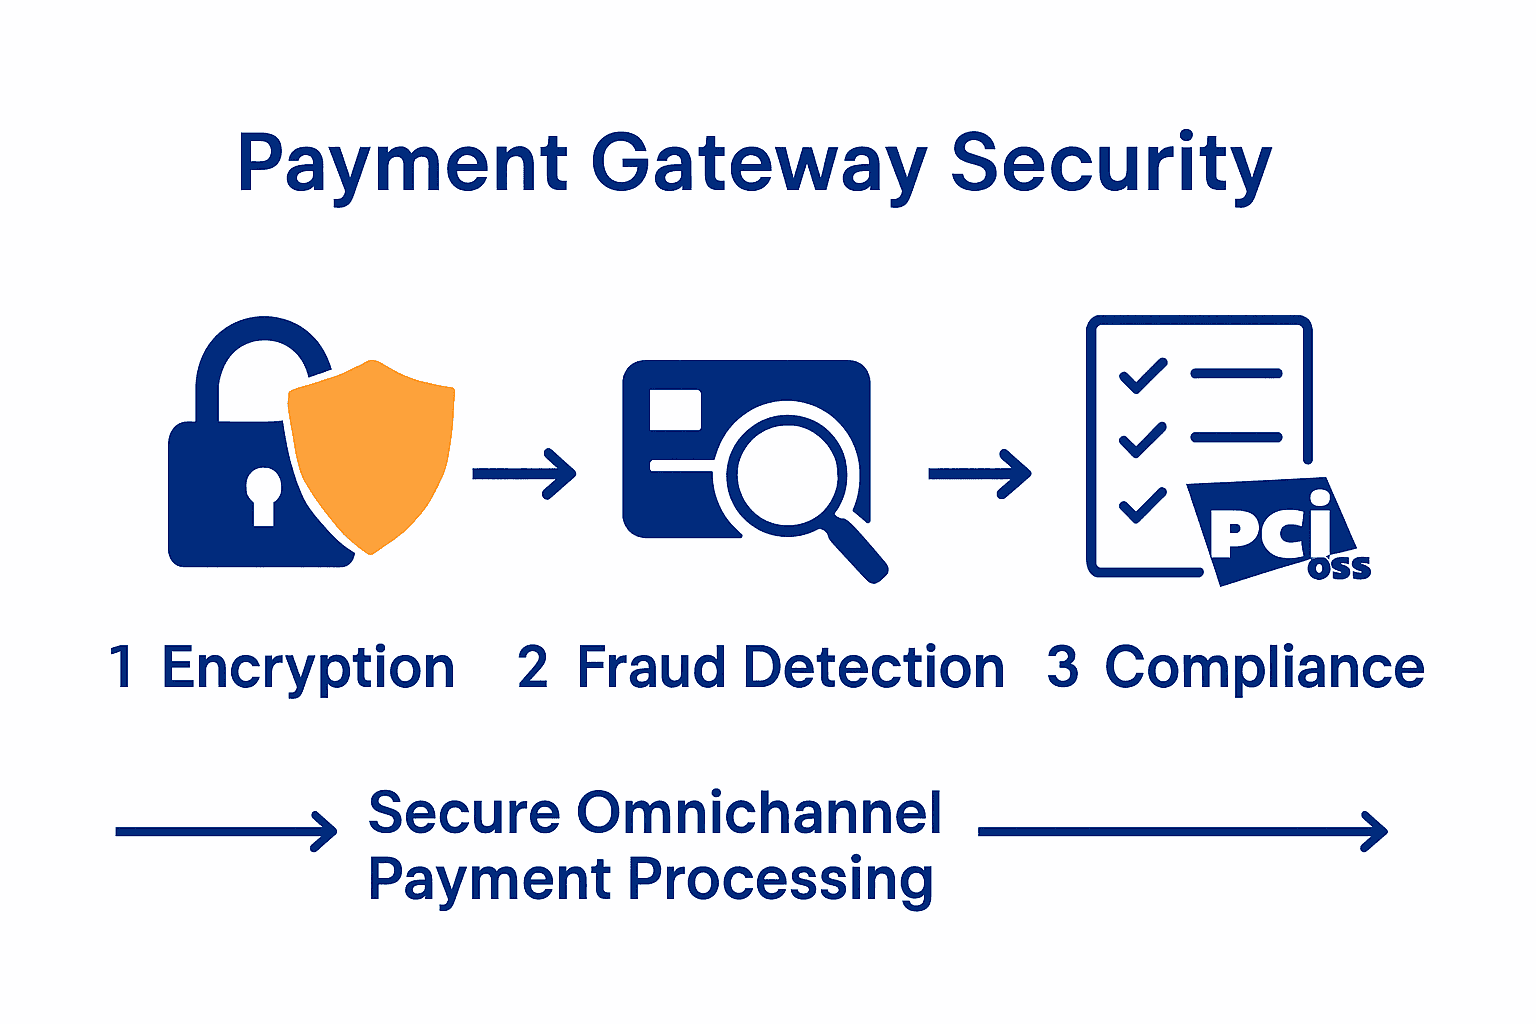
Securing your payment infrastructure requires a comprehensive approach to compliance and encryption that protects customer data across all transaction channels. According to IR, the Payment Card Industry Data Security Standard (PCI DSS) is a globally mandated framework designed to prevent data leaks and protect sensitive financial information from unauthorized access.
To effectively configure omnichannel compliance, implement these critical encryption strategies:
- Encrypt all payment data in transit and at rest
- Use secure TLS protocols for network communications
- Implement tokenization for sensitive customer information
- Create segmented network environments
- Develop robust access control mechanisms
As Wikipedia highlights, PCI DSS compliance involves more than just technical safeguards. It requires annual or quarterly validation to ensure your security protocols remain current and effective. This means regularly reviewing your encryption methods, conducting security audits, and updating your systems to address emerging digital threats.
Understand that compliance is not a one time achievement but an ongoing process. By creating a dynamic encryption strategy that adapts to changing technological landscapes, you build a resilient payment security framework that protects both your business and your customers’ financial data.
Step 5: Monitor Transactions and Test Security Measures
Ensuring the ongoing security of your payment infrastructure requires continuous monitoring and proactive testing of your systems. Federal Reserve guidelines emphasize the importance of establishing clear risk management objectives that allocate acceptable risks and implement strategies to systematically monitor and evaluate security effectiveness.
Develop a comprehensive transaction monitoring approach that includes:
- Real time transaction tracking
- Anomaly detection algorithms
- Automated fraud alert systems
- Regular penetration testing
- Comprehensive transaction log analysis
As Wikipedia explains, control self assessment techniques allow organizations to evaluate risk management processes directly within their operational environment. This means engaging your internal teams to identify potential vulnerabilities, conducting simulated security breach scenarios, and creating adaptive response protocols that can quickly neutralize emerging threats.
Remember that security monitoring is not a static process but a dynamic, evolving strategy. By implementing robust testing mechanisms and maintaining a proactive stance toward potential risks, you transform your payment infrastructure from a potential vulnerability into a resilient and adaptive security ecosystem.
Strengthen Your Omnichannel Payment Security with SensePass
Securing your payment ecosystem across all retail channels is a complex challenge. You need a payment platform that not only supports robust multi-layer authentication and encryption but also offers seamless integration across your systems and payment methods. SensePass solves these pain points by acting as a flexible orchestration layer and next-generation payment gateway built specifically for omnichannel retailers. It supports major platforms like NetSuite, Shopify POS, Oracle Xstore, and Dynamics365, enabling unified management of payments whether in-store, online, or through call centers.
SensePass empowers your business with:
- Wide support of digital wallets including Apple Pay, Google Pay, PayPal, and Amazon Pay
- Flexible payment methods such as Buy Now Pay Later options, crypto payments, and bank transfers
- Processor-agnostic compatibility giving you access to over 50 card processors
If protecting customer data while providing seamless payment experiences is your goal, there is no better time than now to upgrade your payment infrastructure. Learn more about how SensePass can fortify your omnichannel payment security and streamline operations by visiting SensePass.com.
Ready to enhance your payment security and customer satisfaction?

Discover the future of safe and flexible payments at SensePass. Don’t wait until vulnerabilities impact your business. Take control today.
Frequently Asked Questions
What are the key steps to assess payment system risks for omnichannel retailers?
To assess payment system risks, conduct a comprehensive audit of your current payment ecosystem. Map out transaction touchpoints and evaluate each for security gaps, such as weak authentication protocols or unsecured connections.
How can I implement multi-layered payment authentication effectively?
Implement multiple authentication checkpoints that verify customer identity through various methods, such as biometric verification or OTP generation. Start by choosing at least two authentication methods that balance security and user convenience to enhance your transaction security.
What are best practices for selecting secure payment gateways?
Choose payment gateways that offer robust encryption standards and comprehensive fraud detection mechanisms. Focus on gateways that allow seamless integration while ensuring end-to-end transaction protection, making your setup more resilient against threats.
How do I ensure compliance with payment security standards in my omnichannel retail operations?
Ensure compliance with payment security standards by implementing encryption for all payment data and conducting regular security audits. Establish a routine review process to verify compliance, ideally on a quarterly basis, to maintain effective security protocols.
What monitoring strategies should I use to constantly secure my payment transactions?
Develop a real-time monitoring approach that includes anomaly detection and automated fraud alerts. Set up comprehensive transaction logs and conduct regular penetration testing to identify potential vulnerabilities promptly.
How can I improve my payment infrastructure’s resilience against evolving digital threats?
Improve your payment infrastructure’s resilience by adopting a proactive security strategy that includes ongoing testing and adaptive response protocols. Regularly update your systems and monitoring methods to address new threats as they emerge, aiming for updates at least every 30–60 days.
Recommended
- 7 Essential Tips for Your Omnichannel Payment Methods List – Omnichannel payments at the Point Of Sale | Sensepass
- Complete Guide to Omnichannel Payments for Retailers – Omnichannel payments at the Point Of Sale | Sensepass
- What Is Omnichannel Payment? Complete Guide for Retailers – Omnichannel payments at the Point Of Sale | Sensepass
- What Is E-Commerce Business? Complete Guide – Prosperual

 New York Office
260 Madison Ave Suite 8018 New York NY 10016

